vulnhub-xxe漏洞复线
环境搭建
[镜像下载]
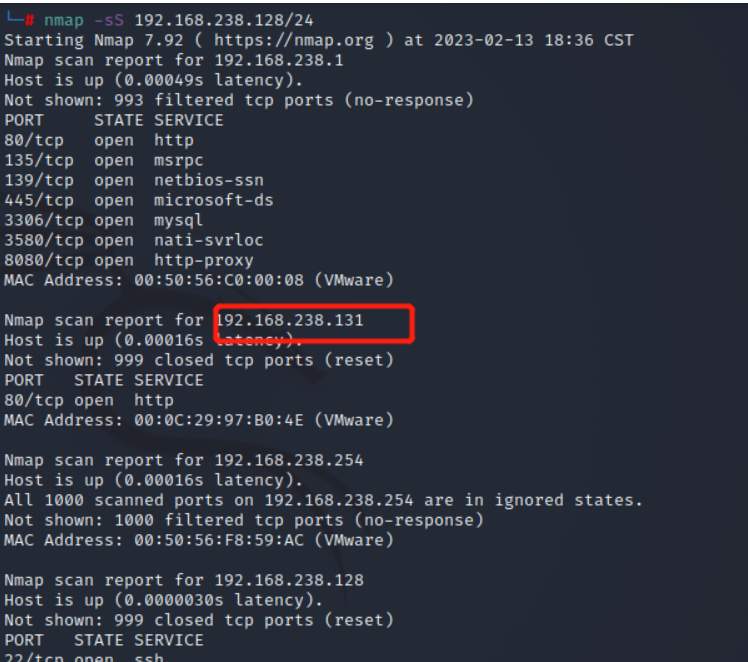
nmap扫描靶机IP
靶机ip为192.168.238.131,并且存在http服务,80端口打开
浏览器访问192.168.238.131
访问只存在ununtu的apache2的默认界面
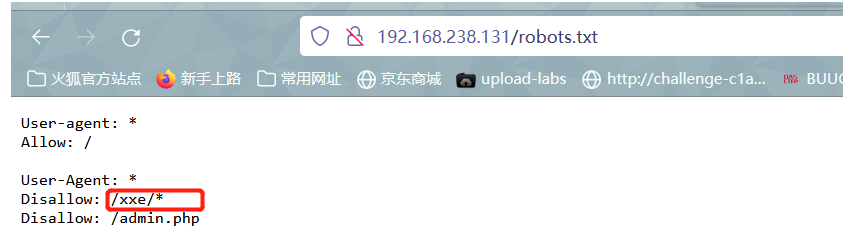
访问192.168.238.131/robots.txt
(robots.txt文件告诉蜘蛛程序在服务器上什么文件是可以被查看的。 )
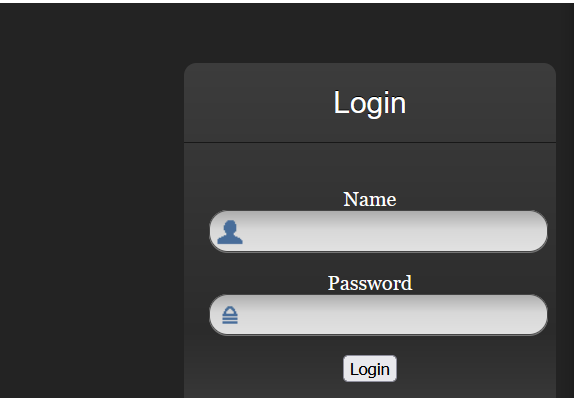
紧接着访问/xxe,发现登录界面
burpsuites抓包
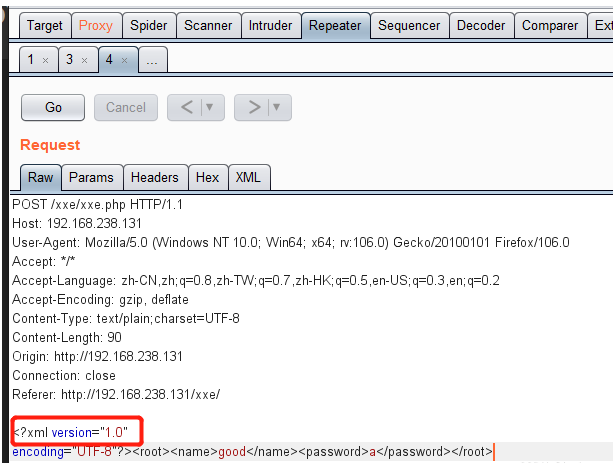
发现传入数据为xml语言数据传输格式
打入payload读取xxe.php
1 | |
返回数据发现xxe.php
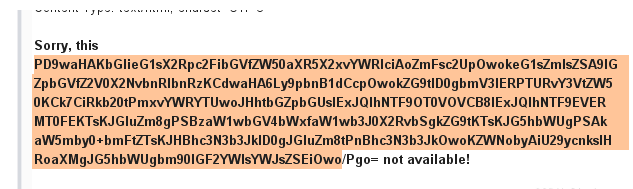
用burpsuite自带的解码工具解码返回的xxe.php代码
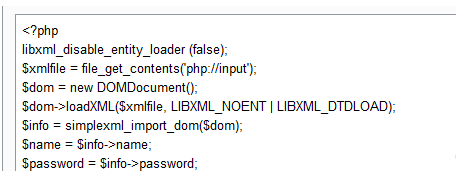
读取admin.php,查看代码用户名为administhebest密码的md5值为e6e061838856bf47e1de730719fb2609解密后为admin@123
 <?php
            $msg = '';
            if (isset($_POST['login']) && !empty($_POST['username'])
               && !empty($_POST['password'])) {
          if ($_POST['username'] == 'administhebest' &&
              md5($_POST['password']) == 'e6e061838856bf47e1de730719fb2609') {
              $_SESSION['valid'] = true;
              $_SESSION['timeout'] = time();
              $_SESSION['username'] = 'administhebest';

            echo "You have entered valid use name and password <br />";
    $flag = "Here is the <a style='color:FF0000;' href='/flagmeout.php'>Flag</a>";
    echo $flag;
           }else {
              $msg = 'Maybe Later';
           }
        }
     ?>
  </div> <!-- W00t/W00t -->

  <div class = "container">

     <form class = "form-signin" role = "form"
        action = "<?php echo htmlspecialchars($_SERVER['PHP_SELF']);
        ?>" method = "post">
        <h4 class = "form-signin-heading"><?php echo $msg; ?></h4>
        <input type = "text" class = "form-control"
           name = "username"
           required autofocus></br>
        <input type = "password" class = "form-control"
           name = "password" required>
        <button class = "btn btn-lg btn-primary btn-block" type = "submit"
           name = "login">Login</button>
登录:
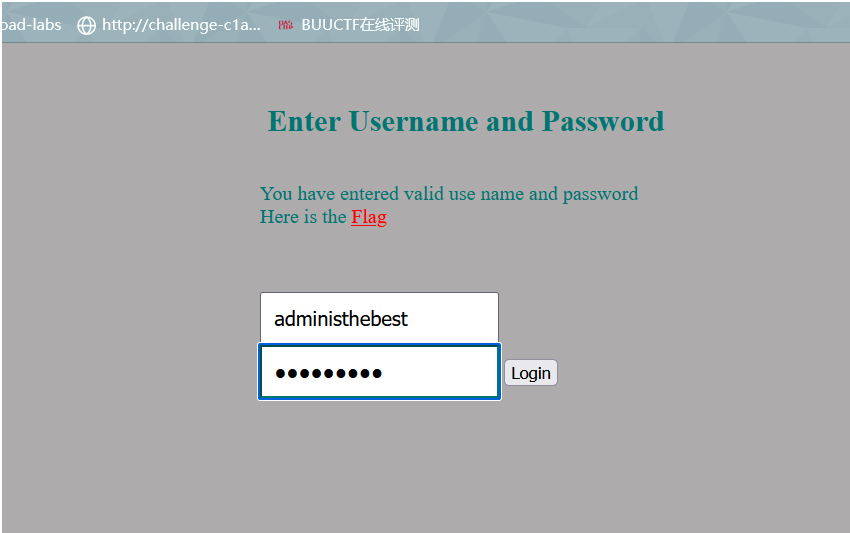
找到新的敏感文件
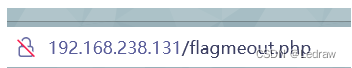
打入payload
1 | |
读取flagmeout.php
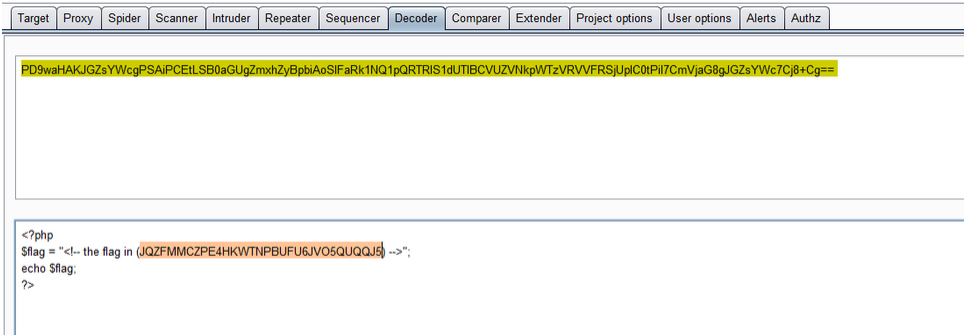
通过判断加密方式为base32编码,先base32解码
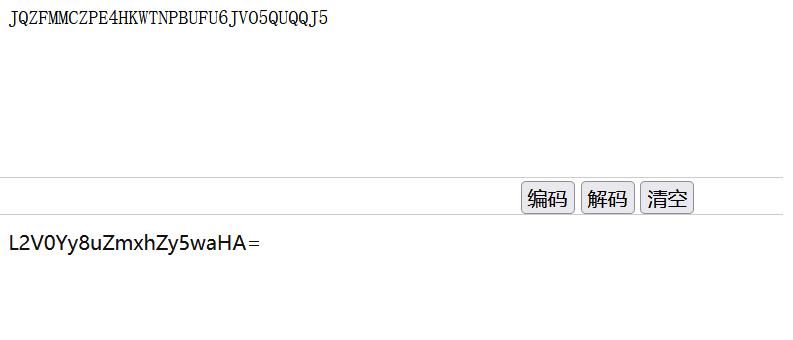
读取/etc/.falg.php
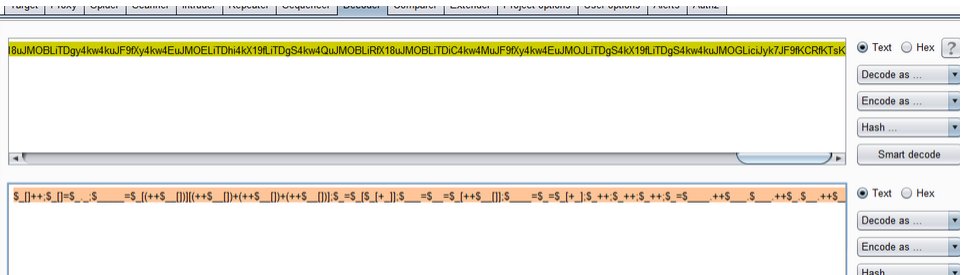
1 | |
解密后发现像php
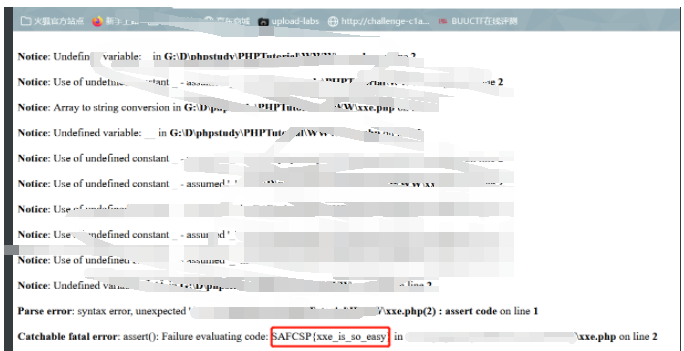
自己写php代码运行,密码为SAFCSP{xxe_is_so_easy}
vulnhub-xxe漏洞复线
https://ledraw.github.io/2024/09/27/vulhub-xxe漏洞复现/